Recrutez avec plus de clarté
Allez au-delà du CV.
Évaluez les compétences.
Transformez votre fiche de poste en test de compétences ou en entretien avec l’IA. Obtenez des rapports clairs avant votre premier échange.
Pour les dirigeants, managers, équipes RH et cabinets de recrutement.
3 candidats gratuits. Sans abonnement.
Comment ça marche
De la fiche de poste à la présélection en cinq étapes
Aucune installation. Aucun compte à créer pour les candidats.
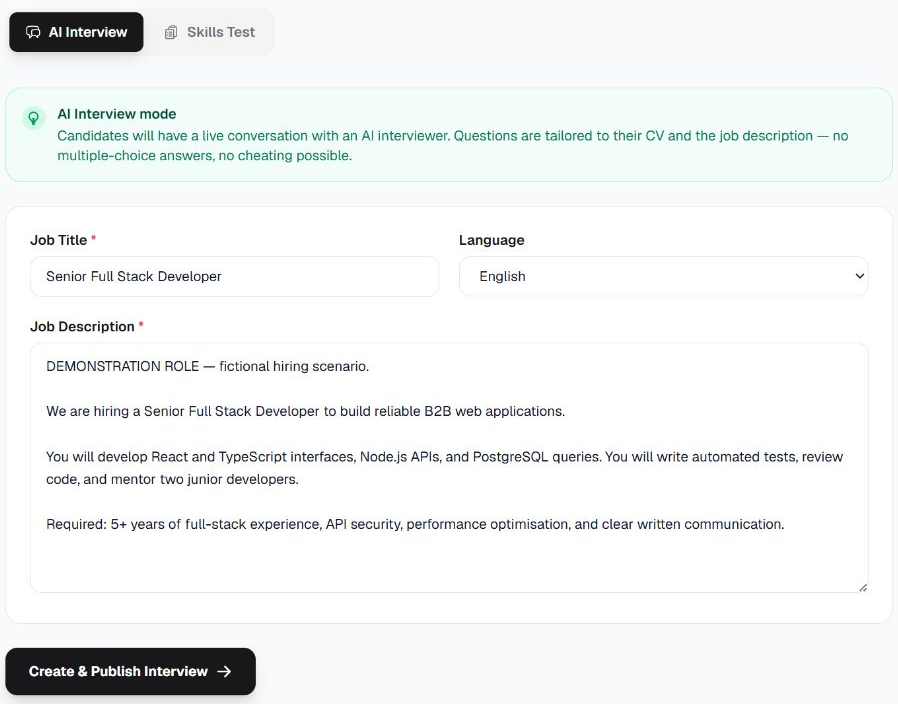
Créez une évaluation adaptée à votre poste
Ajoutez votre fiche de poste, choisissez un test QCM ou un entretien IA, puis la langue.
- Évaluation et rapports dans la langue choisie
- Mode QCM : vérifiez et régénérez les questions
- Anglais, français ou espagnol
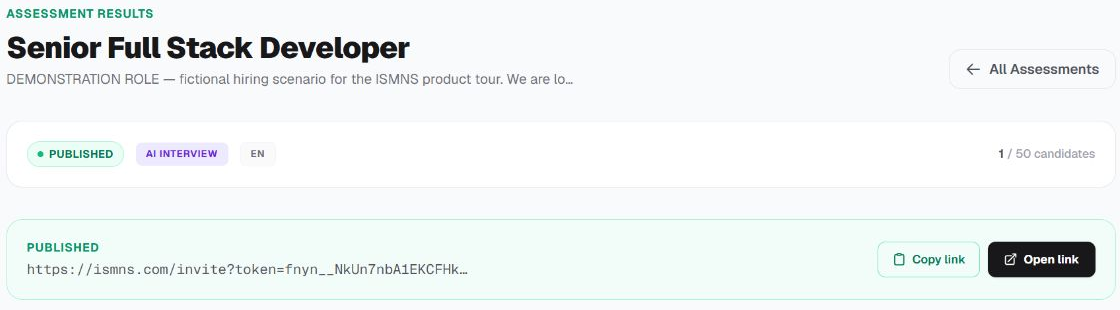
Envoyez le lien aux candidats
Partagez le lien de votre évaluation. Les candidats l’ouvrent et commencent, sans créer de compte.
- Aucun compte pour les candidats
- Accessible sur mobile
- Un lien par poste
Évaluez les compétences en contexte
Les candidats passent un QCM adapté au poste ou un entretien IA qui prend en compte votre fiche de poste, leur CV et leurs réponses.
- QCM chronométré avec questions aléatoires
- L’IA adapte ses questions aux réponses du candidat
- CV et conversation de l’entretien conservés
AI Interview
Recorded demo · 21 messages
- AI interviewer:
Hello Alex, thank you for joining the interview today. Let's dive right into our first topic. Can you describe a specific situation where you optimized a PostgreSQL query for performance? What was the issue, and how did you resolve it?
- Candidate:
In the fictional Demo Studio project, a tenant dashboard endpoint had a p95 latency of about 900 ms. I used query logs and EXPLAIN (ANALYZE, BUFFERS) on representative data to find an N+1 query pattern and repeated scans when filtering by tenant and date. I replaced per-row lookups with a single scoped query and added a composite index matching the filter and sort order. I checked tenant isolation and compared results before and after the change. In our synthetic example, p95 fell to 280 ms under the same workload. I also monitored write overhead and retained a rollback plan.
- AI interviewer:
Thanks for sharing that example, Alex. Let's move on to the next topic. Can you explain how you ensure API security when developing Node.js applications?
- Candidate:
I separate authentication from authorization. Each endpoint checks the authenticated user, their role and the tenant that owns the requested resource; a client-supplied tenant ID is never trusted on its own. I validate request schemas, use parameterized SQL and return only necessary fields. Secrets stay outside source code, tokens have short lifetimes, and cookies use secure settings where applicable. I add rate limits and safe error handling, and redact secrets from logs. In the demo project, integration tests include cross-tenant access attempts, expired sessions and malformed input. Dependency updates and security review are part of CI and release planning.
- AI interviewer:
Great, that provides a clear picture of your approach to API security. Now, let's discuss your experience with React and TypeScript. Could you describe a challenging feature you implemented using these technologies and the steps you took to overcome any difficulties?
- Candidate:
In the demo dashboard, I built a searchable table whose filters were shared with the URL. The difficult part was keeping fast typing, server requests and browser back navigation consistent. I used a typed filter model and runtime validation for URL values, kept draft input local, and debounced requests. I cancelled obsolete requests and ignored stale responses. I added keyboard navigation, explicit loading and empty states, and tests for back navigation and out-of-order responses. I chose simple components over a large state library because the state was confined to one feature.
- AI interviewer:
Thank you for that detailed explanation. Moving on, can you describe your approach to writing automated tests? How do you ensure they are effective and maintainable over time?
- Candidate:
I start from risks and observable behaviour. Unit tests cover deterministic business rules; integration tests exercise APIs with a real test database; a small set of Playwright journeys covers sign-in, tenant boundaries and critical workflows. I avoid coupling tests to component internals and use stable fixtures with explicit setup. When fixing a bug I add a regression case that fails for the original reason. CI runs fast checks on each change and slower suites separately. I investigate flaky tests instead of repeatedly rerunning them, and remove redundant tests when they no longer protect a meaningful behaviour.
- AI interviewer:
That's a solid approach to automated testing. Let's shift gears a bit. Could you tell me about a time when you had to mentor a junior developer? What strategies did you use to help them grow?
- Candidate:
In the fictional team, a junior developer struggled to diagnose intermittent API failures. We agreed on a small learning goal: turn an unclear bug report into a reproducible test. During pairing, I asked them to explain their hypothesis, inspect logs and narrow the input rather than taking over. We then wrote the regression test and a short debugging note together. In later reviews I separated blocking issues from suggestions and explained the reason behind each comment. We reduced pairing gradually as they became independent. I would assess progress through the problems they could solve and the questions they asked, not the number of lines written.
- AI interviewer:
Thank you for sharing that experience. Let's talk about performance optimization. Can you give an example of how you've improved the performance of a Node.js application? What specific techniques did you use?
- Candidate:
For a fictional CSV export feature, synchronous parsing and serialization caused event-loop delays that affected other requests. I measured event-loop lag, CPU usage and endpoint latency before changing the code. I moved long exports to a bounded background queue, streamed the output and applied backpressure instead of holding the whole dataset in memory. The API returned a job reference and the UI displayed progress. I capped concurrency to protect the database and tested failure recovery and duplicate requests. The trade-off was an asynchronous user flow, so we agreed on that behaviour with the product team. I would compare p95 latency, memory and error rates under the same load before claiming an improvement.
- AI interviewer:
That's a comprehensive approach to optimizing performance. Now, let's verify a specific claim from your CV. You mentioned working on integrating Jest tests and CI checks. Can you elaborate on how you set up these systems and how they benefited the development process?
- Candidate:
For the fictional Sample Works project, I configured Jest for fast TypeScript business-logic tests and a separate integration suite against an isolated PostgreSQL database. The CI pipeline installed locked dependencies, checked formatting and types, ran unit tests, then integration tests and a production build. Each test run used its own database state and secrets were injected by the CI environment. Pull requests could not merge if required checks failed. We added coverage for tenant boundaries and export retries after identifying risks, rather than chasing a coverage percentage. The benefit was earlier feedback and reproducible failures; I would track escaped regressions and flaky-test frequency to see whether it helped.
- AI interviewer:
Thank you for that detailed explanation. Now, let's explore a soft skill. How do you approach problem-solving when faced with a particularly challenging technical issue? Can you provide an example?
- Candidate:
I first describe the observed behaviour, impact and constraints, then list a few testable hypotheses. I reproduce the issue with the smallest useful case and change one variable at a time. In the fictional dashboard, users sometimes saw old search results after typing quickly. I used network timings to show that responses arrived out of order. I added request cancellation and a current-request guard, then a test that deliberately reversed response order. I shared a short explanation with the team and checked the fix with the designer. If evidence contradicts my hypothesis, I change direction; if I am stuck, I ask a colleague with a concise reproduction instead of hiding the delay.
- AI interviewer:
That's a thoughtful approach to problem-solving. Let's discuss collaboration. Can you share an example of how you've worked with a cross-functional team to deliver a project? What challenges did you face, and how did you overcome them?
- Candidate:
For the demo export feature, I worked with a designer, product manager and support colleague. The initial request was an instant download, but large datasets made that unreliable. I explained the constraint with measurements and proposed a background export with clear status and a retry option. We agreed on acceptance criteria for accessibility, completion time and failure messages, then released a small version behind a feature flag. Weekly demos exposed misunderstandings early. When scope grew, I made the delivery trade-offs explicit and let the product manager choose priorities. I documented the final decision and a rollback procedure for the team.
- AI interviewer:
Thank you for sharing that collaborative experience. Lastly, I'd like to discuss code reviews. How do you approach reviewing code from others to ensure quality and consistency?
- Candidate:
I first understand the intended behaviour and read the change in context. I check correctness, security boundaries, error handling, accessibility and meaningful tests before style. Automated formatting handles routine consistency so comments can focus on decisions. I label blocking issues and optional suggestions, explain the reason, and ask questions when I lack context. I keep reviews small and timely; for a complex design disagreement I propose a short discussion and record the outcome. In the demo team, a recurring checklist covered tenant isolation and database migrations. I also review my own assumptions and accept a simpler solution when it meets the requirements.
- AI interviewer:
Thank you, Alex, for all the detailed insights you've provided today. I appreciate you taking the time to discuss your experiences and skills with me. We'll be in touch soon regarding the next steps. Have a great day!
Fictional candidate · Preview only — no answers are sent
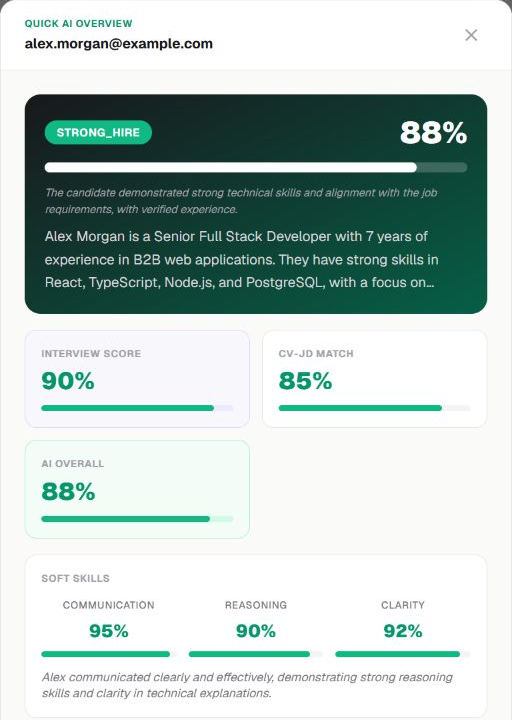
Identifiez les candidats à rencontrer
Les candidats sont évalués et classés à mesure qu’ils terminent. L’aperçu rapide présente le score, les points à approfondir et la recommandation.
- Classement en direct
- Points forts, lacunes et adéquation du CV
- Une recommandation pour éclairer votre décision
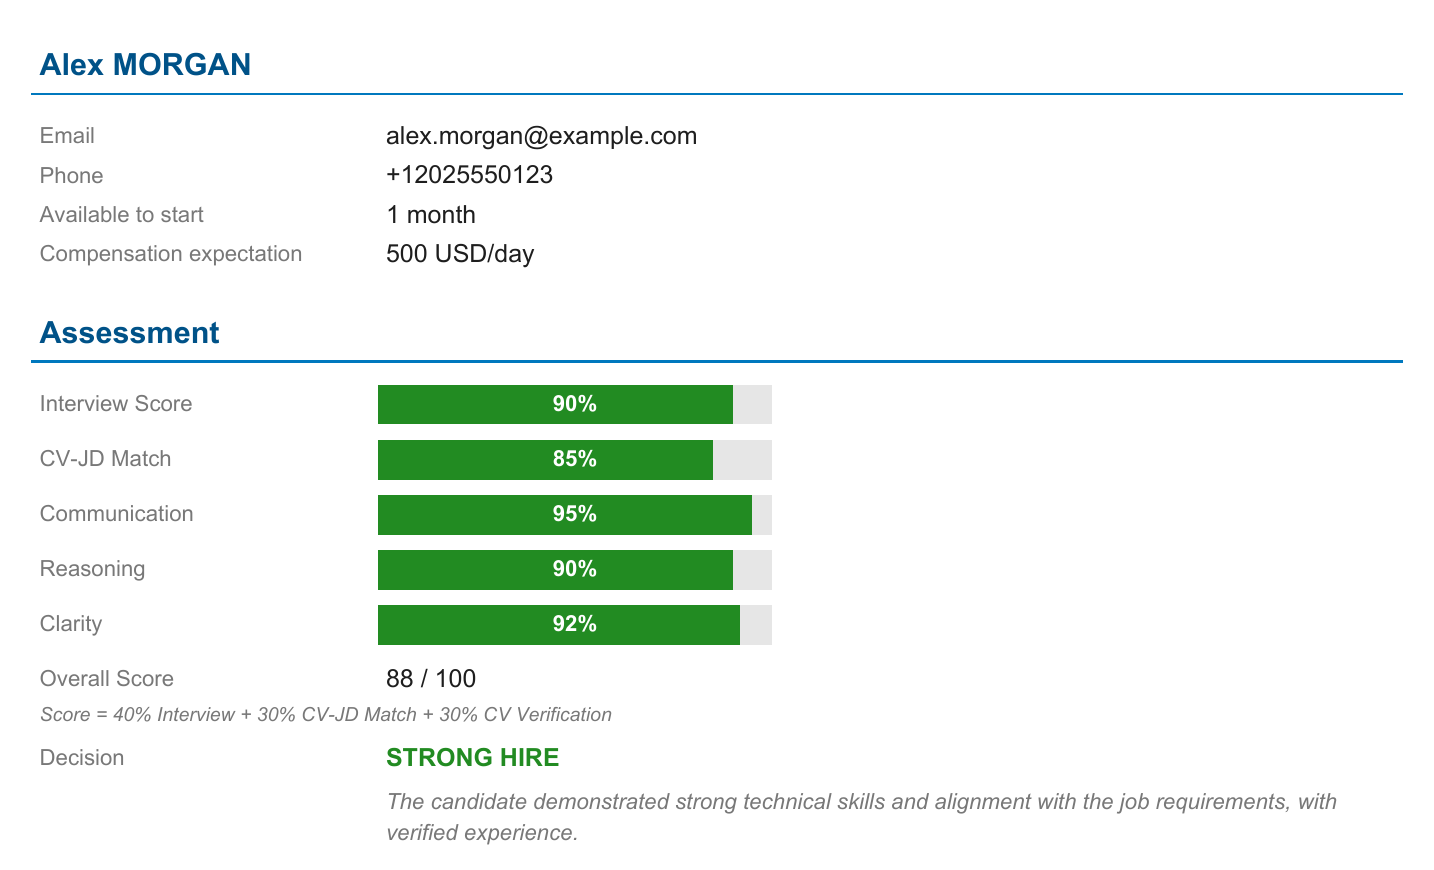
Contactez les candidats les plus pertinents
Retrouvez les résultats, l’analyse du CV et les points à approfondir dans un rapport clair pour choisir les candidats à contacter.
- Prêt à partager
- Facile à archiver
- Le même format pour chaque candidat
Pourquoi choisir ISMNS
Les éléments pour décider. Avant le premier échange.
Chaque évaluation est créée pour votre poste. Pour chaque candidat, retrouvez les compétences évaluées, l’analyse du CV, la rémunération souhaitée et les disponibilités. Choisissez qui rencontrer avec ces informations en main.
À partir de $1.79 par candidat. Moins qu’un appel de présélection, et vous payez uniquement pour les candidats évalués.
Compétences évaluées
Un score pour chaque compétence de votre offre, fondé sur l’évaluation.
CV analysé
Une analyse par rapport au poste : points forts, lacunes et expérience pertinente.
Rémunération et disponibilité
Salaire ou tarif journalier souhaité et date de disponibilité, recueillis avant votre appel.
Adéquation et recommandation
Compétences comportementales, recommandation et un PDF à transmettre.
Deux modes d’évaluation
Test de compétences ou entretien avec l’IA : choisissez selon le poste
Un test pour les recrutements en volume. Un entretien pour les profils seniors ou en relation client.
Test de compétences
Un QCM chronométré créé à partir de votre offre. Rapide à passer et à corriger, avec des contrôles anti-triche.
- Questions générées à partir de l’offre
- Vérification et régénération avant publication
- Chronométrage, ordre aléatoire et détection de triche
- Seuil de réussite automatique
- Score par compétence
Idéal pour
Postes techniques, recrutements en volume et présélection standardisée
Entretien avec l’IA
Une conversation écrite adaptée au CV et aux réponses du candidat. Elle évalue ses connaissances et sa façon de les expliquer.
- Questions adaptées en temps réel
- Compétences techniques et comportementales
- Clarté et raisonnement évalués
- Détection des changements d’onglet et du collage
Idéal pour
Postes seniors, relation client et fonctions où la communication compte
Vous hésitez ? Un test pour le volume, un entretien pour les trois finalistes. Le tarif reste le même.
Tarifs
Par candidat, moins qu’un appel de présélection.
Un pack par poste, à partir de $39. Sans abonnement, sans licence par utilisateur, sans catalogue de tests. Remboursement sous 7 jours si personne n’a commencé.
Idéal pour un premier recrutement ou une présélection
- ✓Test de compétences ou entretien avec l’IA
- ✓Évaluation adaptée à la fiche de poste
- ✓Rapport PDF et analyse du CV
Adapté à un poste avec de nombreuses candidatures
- ✓Test de compétences ou entretien avec l’IA
- ✓Évaluation adaptée à la fiche de poste
- ✓Rapport PDF et analyse du CV
Pour les présélections en volume
- ✓Test de compétences ou entretien avec l’IA
- ✓Évaluation adaptée à la fiche de poste
- ✓Rapport PDF et analyse du CV
Recrutement à grande échelle, sur mesure
- ✓Test de compétences ou entretien avec l’IA
- ✓Évaluation adaptée à la fiche de poste
- ✓Rapport PDF et analyse du CV
Une évaluation par pack : test de compétences ou entretien avec l’IA. Analyse du CV et rapports PDF inclus. Voir le détail des tarifs et les conditions de remboursement
FAQ
Questions fréquentes
Test de compétences ou entretien avec l’IA : quelle différence ?
Le test de compétences est un QCM chronométré sur les compétences techniques. L’entretien avec l’IA est une conversation écrite adaptée au CV et aux réponses, qui évalue aussi les compétences comportementales.
Que contient le rapport PDF ?
Scores par compétence, analyse du CV, points forts et lacunes, disponibilité, rémunération et recommandation. Les rapports d’entretien ajoutent des scores de communication, de raisonnement et de clarté.
Puis-je modifier les questions ?
Oui. Vérifiez chaque question avant publication et régénérez celles qui ne vous conviennent pas.
Quelles langues sont disponibles ?
Anglais, français et espagnol. Les tests et entretiens sont générés directement dans la langue choisie.
Les candidats doivent-ils créer un compte ?
Non. Ils ouvrent le lien, indiquent leur e-mail et commencent, sur l’appareil de leur choix.
Les données des candidats sont-elles protégées ?
Les données sont chiffrées en transit et au repos. Seul le recruteur qui a créé l’évaluation peut les consulter.
Comment fonctionne l’entretien avec l’IA ?
L’IA analyse votre offre et le CV du candidat, puis mène un entretien écrit en direct. Les relances s’adaptent à chaque réponse.
Comment fonctionnent les tarifs ?
Un pack par poste, à partir de 39 $ pour 15 candidats. Sans abonnement ni frais cachés. Consultez les tarifs pour les conditions de remboursement.
Quelle différence avec les banques de tests ou les entretiens vidéo ?
L’évaluation est générée pour votre poste en quelques minutes, sans catalogue de tests génériques ni licence par utilisateur. L’entretien est écrit et adaptatif : les candidats n’ont pas à s’enregistrer en vidéo.
Puis-je essayer avant d’acheter ?
Oui. Profitez d’un pack d’essai gratuit pour 3 candidats, accordé une seule fois. Créez un test de compétences ou un entretien avec l’IA et consultez les résultats et rapports. Achetez un pack lorsque vous avez besoin d’évaluer davantage de candidats.
Votre premier échange, avec le bon candidat.
Commencez avec 3 candidats gratuits. Collez votre fiche de poste, partagez le lien d’évaluation et consultez les résultats et le rapport de chaque candidat.